The Zero Trust Hub
Trends, insights, and resources for today's cybersecurity leaders. Updated weekly.
On the N2K CyberWire podcast, John Kindervag, the creator of Zero Trust, explains why AI-powered attacks call for faster defenses. He shares how a Zero Trust strategy and automation can help security teams catch and contain threats fast and build lasting cyber resilience.

In SecurityWeek, Federal CTO Gary Barlet warns about a recent leak of more than 41,000 DHS employee records. The data shows how agency staff reach key internal systems each day. Attackers could use it as a ready-made roadmap to plan their next cyberattack.
Taking Trust for Granted: How Nation-State Influence Exploits Implicit Trust
Public Sector CTO
When people ask me about nation-state threats on Election Day, they usually picture the same scene. A hacker in a dark room breaks into a voting machine and quietly flips votes to put a favored candidate in office.
It makes a great movie plot. But after 20 years as a cyberspace operations officer in the Air Force and a long career in federal IT, I’ve seen that influence campaigns usually aim at something softer and easier to reach. They go after the shortcuts we all use to decide what's true, like a blue check mark, a pile of likes, or a video that looks too real to question.
Those shortcuts are a form of implicit trust, and attackers exploit the same weakness inside corporate networks. As voters head to the polls on November 3, the lesson for security leaders is simple.
Zero Trust works because it swaps assumptions for verification, and that habit is the best defense against nation-state influence, whether it targets a voter’s feed or your network.
Seeing is no longer believing
Not long ago, a photo or video was close to proof. Today, just because I see something with my own eyes doesn’t make it true. AI tools can create a convincing fake image, voice clip, or video in minutes.
Influence campaigns only need content that looks real enough to get shared before anyone checks it. Once it spreads, the damage is done, even if someone debunks it a day later.
Everyone wants an easy button
Most people won’t spend much time researching what they see online. We look for an easy button, some sign that someone else already did the work and we can trust it.
Security teams know this pattern well, because networks ran on easy buttons for years. A device on the corporate network, a valid login, or a familiar IP address meant a system was trusted. Attackers count on that. Once they get a foothold, they use that built-in trust to move from system to system.
Elections face the same risk. In its 2026 election security plan, CISA noted that election systems are often reachable from general business networks, which lets attackers exploit known flaws and move laterally.
Validation you can scale
I’d like to see more AI tools that check a claim against other sources and give it a confidence score. Something like, “I can’t find this anywhere else, and no news outlet has reported it.” That kind of seal confirms the content has been checked and appears legitimate, without taking a side on what it says.
Human researchers can’t keep up with the flood of content, so this work needs automation.
That’s how Zero Trust works inside a network, too. Every request gets checked based on who’s asking and what they need, every time. Microsegmentation enforces least-privilege access, so even when something slips through, it can only reach what it’s allowed to reach.
Take a beat before you pass it on
For individuals, the best defense is a pause. If something sounds sensational, check it first, and don’t let your own bias lead you down a path. Run a quick search to see if it shows up anywhere else, or ask your favorite AI model to help validate it. You’ll often find something that debunks it right away.
Security teams need the same habit. When an alert, a claim, or a strange request lands on your desk, verify it before you act. And plan for the moments when something gets past you. Breach containment helps keep one bad decision from turning into a much bigger problem.
Implicit trust is a risk you can’t afford to keep
The volume of AI-generated content is growing faster than any person or team can review it. Influence campaigns also don’t end when the polls close.
Any organization that depends on public confidence, from banks and hospitals to utilities and agencies, is a target every day of the year.
In my career, I’ve learned that adversaries go after whatever we take for granted. Right now, that’s implicit trust in what we see online and in what’s already inside our networks.
Every month AI makes a fake easier to produce and harder to spot, and every month an organization runs on implicit trust, it hands attackers more room to work.
STATSHOT
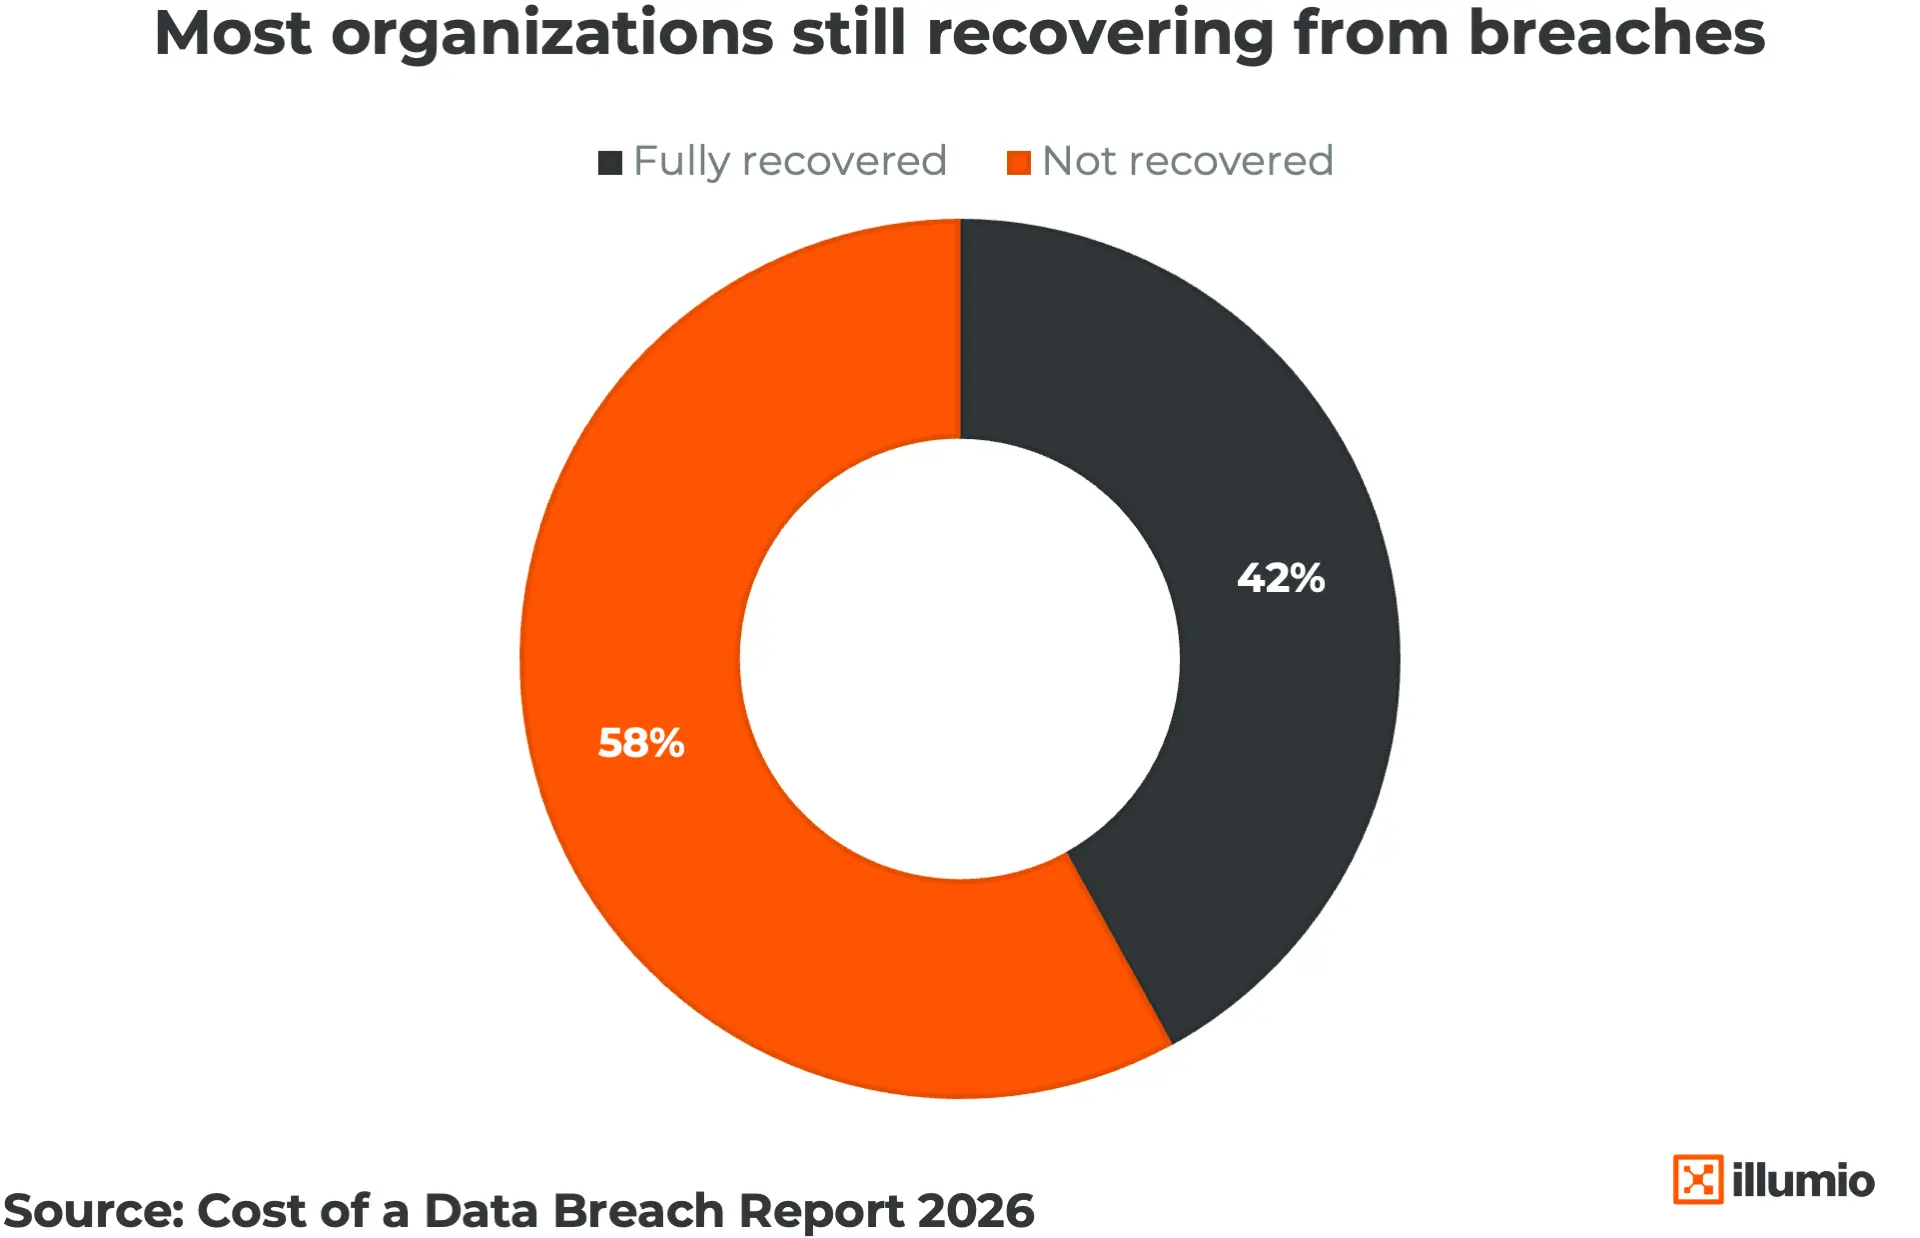
Damage Control
Breached organizations made progress toward full recovery in 2026. The share reporting complete recovery rose to 42%, up from 35% in 2025. Yet 58% had not fully recovered. Restoring operations is only part of the challenge. Organizations must also meet compliance obligations, rebuild trust, and strengthen defenses. For many, recovery can take months or even years.
Last Call: How Qilin Tapped Into a Beer Maker’s Network
One weak password gave attackers about 10 days inside a Japanese beverage maker’s network before they encrypted its systems. Learn how manufacturers can limit lateral movement and keep one compromised system from halting production.
Shell Shocked: AI Turns an Old PHP Bug Into a Crisis
A PHP flaw sat unresolved for two years until AI-assisted research turned it into a working exploit, putting more than 22.6 million servers at risk. This blog post details the attack and explains why patching is only the first move toward containing breaches.
Zero Trust Resources
Get the industry’s first vendor-neutral Zero Trust certification.